

Penetration testing prices vary because a quote covers a scope, not a standard package. A small external assessment and a white-box review of a multi-service application require different access, testing depth, and deliverables.
All three say they use AI. All three promise a comprehensive report. All three look credible.
The difference between them, including the difference between finding an authentication bypass that exposes customer records and missing it entirely, is not always visible in the quote.
It lives in methodology: what the tester actually does, which vulnerability classes are in scope, whether findings are manually validated, whether exploitability is demonstrated, and whether the final output provides the evidence your security and compliance teams actually need.
This guide breaks down real penetration testing costs in 2026 by test type, explains the variables that drive price up or down, and, most importantly, tells you what you are actually buying at each tier so you can evaluate quotes against what you need rather than what sounds reasonable.
Quick Answer: How Much Does Penetration Testing Cost in 2026?
For planning purposes, penetration testing can range from approximately $3,000 for a limited external assessment to $100,000+ for a large, integrated assessment covering black box, white box, gray box, applications, APIs, and infrastructure.
Typical planning ranges include:
Penetration test type | Typical 2026 cost |
|---|---|
Black box web application assessment | $3,000 to $25,000 |
White box / source code assessment | $15,000 to $60,000 |
Gray box assessment | $10,000 to $40,000 |
Full black + white + gray box assessment | $25,000 to $100,000+ |
Continuous / monthly assessment | $5,000 to $20,000/month |
These are planning ranges, not standardized market prices. Actual penetration testing pricing depends on application size, number of assets, testing methodology, authentication requirements, source-code access, infrastructure complexity, retesting, reporting, and compliance requirements.
What Actually Drives Penetration Testing Cost
Before comparing prices, understand the variables. Penetration testing pricing is primarily driven by scope, test type, methodology depth, and deliverables.
Scope is the largest single cost driver and the most commonly manipulated variable in competitive quotes. A single web application is not the same scope as that application plus its API layer plus the cloud infrastructure it runs on plus the source code repository. Quotes that look similar often scope differently, one firm is testing the login page and a handful of authenticated endpoints; another is testing every subdomain, every API endpoint, every cloud storage bucket, and scanning the complete Git history. Always demand a written scope document before comparing penetration testing quotes. “Your web application” is not a scope.
Test type drives cost because different types require fundamentally different methodology depth. A black box external assessment requires reconnaissance and external surface testing. A white box engagement requires reading and reasoning about source code, tracing data flows, analyzing authentication configurations, scanning commit history. That takes substantially more time. A full assessment covering all three types (black, white, gray box) is a different engagement category entirely. For a deeper breakdown, see The 3 Types of Penetration Testing and How to Pick the Right One.
Methodology depth is what most buyers cannot assess from a quote, and it is what determines whether the report produces actionable evidence or compliance theater. Does the firm confirm exploitation with working proof-of-exploit before reporting a finding, or does it report signature-matched potential findings? Does it construct exploit chains across findings, or report each finding in isolation? Does it trace vulnerabilities to root cause at the file and line level, or provide generic remediation advice?
The $6,500 quote and the $22,000 quote can describe the same scope with entirely different methodology depth. The way to evaluate is to ask for a sample finding from a previous engagement. A real finding looks like this:
A finding without root cause to file and line, without working proof-of-concept, and without a specific remediation diff is not actionable. Your engineers will spend two hours debugging before they can fix it.
Deliverables are the fourth cost driver, and the one that creates the most expensive surprises. For SOC 2 Type II compliance, you need a retest report confirming remediations were independently verified in production, timeline documentation for every finding, risk acceptance records for anything unresolved, and a data deletion certificate. Many firms charge extra for retesting. Some do not produce timeline documentation at all. You discover this after the audit, not before.
How Much Does a Penetration Test Cost for a SaaS Startup?
For a SaaS startup, penetration testing cost depends less on the company's size and more on what the assessment actually needs to cover. Application architecture, API surface, authentication, user roles, multi-tenancy, cloud infrastructure, source-code access, and reporting requirements can all change the final price.
As a practical 2026 planning range, a focused SaaS web application penetration test may cost approximately $8,000 to $15,000 when performed by a traditional penetration testing firm. Larger or more technically complex assessments can cost considerably more when they include multiple applications, extensive APIs, cloud infrastructure, source-code review, or deeper authenticated testing.
The important point is that $8,000 and $15,000 may not represent two different prices for the same test. They may represent two different levels of coverage.
What a SaaS Startup Should Expect to Pay
A simplified planning framework looks like this:
SaaS testing requirement | Typical planning range | What can increase the cost |
|---|---|---|
Focused external web application test | $3,000–$8,000 | Larger attack surface, authenticated testing, manual validation |
Comprehensive web application test | $8,000–$15,000 | APIs, multiple roles, business logic, deeper exploitation |
Authenticated / gray box assessment | $10,000–$40,000 | Multiple roles, tenants, workflows, API complexity |
White box / source-code assessment | $15,000–$60,000 | Codebase size, data-flow analysis, infrastructure and CI/CD review |
Integrated assessment | $25,000–$100,000+ | Multiple applications, cloud infrastructure, source code, complex attack paths |
These are planning ranges rather than standardized market prices. Actual penetration testing pricing varies by provider, scope, methodology, testing depth, and deliverables.
What Should Be Included in a SaaS Penetration Test?
Before accepting a quote, a startup should establish whether the assessment covers the parts of the application that actually represent security risk.
At minimum, ask about:
Web applications: Which applications, environments, domains, and subdomains are included?
APIs: Are authenticated and unauthenticated API endpoints tested?
Authentication: Are login, MFA, password reset, sessions, tokens, and account recovery flows tested?
Authorization: Are horizontal and vertical privilege boundaries tested?
Multi-tenancy: Is cross-tenant access explicitly tested?
Business logic: Are application-specific workflows tested manually?
Infrastructure: Are cloud services and exposed infrastructure included?
Source code: Is white-box analysis part of the engagement?
Exploitation: Are suspected vulnerabilities validated through controlled exploitation?
Retesting: Is remediation verification included?
Reporting: What evidence and remediation guidance are included?
This is particularly important for SaaS applications because a vulnerability such as an authorization failure may only become visible when multiple users, roles, tenants, and API objects are tested together. Our guide to IDOR vulnerabilities goes deeper into why these authorization flaws can be missed when testing focuses only on the external attack surface.
When Should a Startup Spend More?
A higher penetration testing budget makes more sense when the application has a larger or more complex security boundary.
Consider deeper testing when your SaaS platform has:
Sensitive customer or financial data
Multiple user roles
Multi-tenant architecture
Hundreds of API endpoints
Administrative functionality
Complex approval or billing workflows
Significant cloud infrastructure
Multiple production services
Frequent deployments
Strict compliance or customer security requirements
For a startup, the goal should not be to buy the most expensive penetration test available. It should be to buy enough testing depth to validate the risks that matter most to the business.
Penetration Testing Cost by Test Type in 2026
Black Box Web Application Penetration Testing Cost: $3,000 to $25,000
The range reflects methodology depth, not scope differences. Understanding what you get at each tier:
$3,000–$8,000: You are buying a scanner run with a structured report. Automated signature matching against known CVEs, potential findings based on version detection, CVSS scores without confirmed exploitation. This can be useful for baseline security visibility, but buyers should verify whether manual exploitation, business logic testing, authenticated testing, and retesting are actually included. Compliance teams should also confirm with their auditor what evidence is expected from the penetration testing engagement.
$8,000–$15,000: A genuine methodology-based black box assessment. DNS enumeration and subdomain discovery, CT log queries, cloud asset enumeration, JS bundle analysis, manual verification of findings, working proof-of-exploit for critical and high findings, structured report with compliance mapping. This is the minimum viable tier for compliance.
$15,000–$25,000: Comprehensive black box coverage. Complete reconnaissance depth including all discovered subdomains and cloud assets, JS bundle secret detection with live verification, full port scan across all discovered hosts, exploit chain construction across findings, researcher validation of every finding. This tier produces the evidence quality that SOC 2 Type II auditors are trained to look for.
White Box / Source Code Penetration Testing Cost: $15,000 to $60,000
White box testing costs more because it is fundamentally more labor-intensive. Reading a codebase, tracing data flows, analyzing authentication configurations, and scanning Git history across a real production codebase takes significantly more time than external testing, and the findings it produces are invisible to any external methodology.
$15,000–$25,000: Focused source code review covering highest-risk files, authentication logic, API controllers, database query construction, CI/CD pipeline configurations. Missing: full dataflow analysis across the complete codebase, Git history scanning, infrastructure configuration review.
$25,000–$40,000: Full codebase review with dataflow tracing. Every user-controlled input traced to every dangerous sink. Every authentication configuration read end-to-end. Security configuration analysis for the specific framework (Spring Security filter chains, Express.js middleware ordering, Django permission classes). Git history scanning for historical credentials.
$40,000–$60,000: Complete white box engagement. Everything above plus: dependency reachability analysis (distinguishing between a CVE in a library that processes every user file upload versus one that is imported but never called), infrastructure-as-code review (Terraform, Kubernetes manifests, Dockerfiles), complete CI/CD pipeline security analysis.
Gray Box Penetration Testing Cost: $10,000 to $40,000
Gray box cost scales with role model complexity and the number of distinct user flows. A two-role application with five core workflows is at the lower end. A multi-tenant SaaS with four role tiers, complex permission inheritance, and dozens of API endpoints per role is at the higher end.
The highest-value gray box finding class, cross-tenant IDOR, requires understanding the data model well enough to systematically test every identifier-accepting endpoint across tenants. This is not something a quick scan produces. It requires building a complete model of what each role is supposed to be able to access and then systematically verifying whether the API enforces it.
Full Penetration Testing Assessment Cost: $25,000 to $100,000+
A full assessment is not three separate engagements added together. It is a single integrated engagement where findings from each track inform the others. Reconnaissance findings from the black box track shape what the gray box track targets. Source code analysis from the white box track informs what chains are possible in the exploit construction phase.
The integrated engagement costs less than three separate engagements because the reconnaissance and reporting phases overlap. Expect $25,000–$50,000 for a mid-size SaaS application with moderate infrastructure complexity, $50,000–$100,000 for larger multi-service applications with complex infrastructure, $100,000+ for enterprise-scale assessments requiring coverage of multiple applications and deep infrastructure analysis.
Continuous Penetration Testing Cost: $5,000 to $20,000 per Month
Monthly continuous testing aligns security testing cadence to deployment velocity. A SaaS team shipping code weekly introduces new attack surface in every release. Annual testing leaves up to 11 months of that surface untested. Monthly assessment closes that gap to 30 days.
Continuous testing also produces the strongest possible SOC 2 Type II evidence: a continuous audit trail of findings, remediations, and verifications across the full observation period, rather than a single point-in-time snapshot. When the auditor asks “what covers Q3 and Q4?,” monthly testing has an answer.
Penetration Testing Cost vs Coverage (2026)
Type | Typical cost | What you get | What you miss |
|---|---|---|---|
Automated scanner | $3,000–$8,000 | CVE list, potential findings, PDF report | Working proof-of-exploit, chain analysis, compliance evidence |
Black box (external only) | $8,000–$25,000 | Recon, JS bundle analysis, API auth testing, cloud assets | Source code vulnerabilities, middleware bypasses, business logic |
White box (source code) | $15,000–$60,000 | Dataflow tracing, auth config analysis, Git history, secrets | Runtime behavior, authenticated user flows |
Gray box (authenticated) | $10,000–$40,000 | IDOR, privilege escalation, JWT manipulation, business logic | External surface, code-level root cause |
Full assessment (all three) | $25,000–$100,000+ | Complete coverage: external + code + authenticated flows | Nothing, this is the complete picture |
Continuous monthly | $5,000–$20,000/mo | Full observation period coverage, SOC 2 Type II evidence trail | Nothing, as long as cadence matches deployment velocity |
Why Cheap Penetration Testing Becomes Expensive
The $6,500 penetration test feels like a win until three things happen, and all three happen consistently.
The audit failure. SOC 2 Type II auditors do not ask whether you ran a penetration test. They ask whether exploitable vulnerabilities were found, remediated, and independently verified. A scanner-based report with no working proof-of-exploit does not satisfy that question. The auditor marks CC7.1 as having an exception. That exception appears in your SOC 2 report. Every enterprise buyer you send that report to reads the exceptions section first. The $6,500 test just cost you a deal.
The retest bill. Traditional penetration testing firms charge for the initial engagement. Retesting is almost universally a separate line item, typically 30–40% of the original engagement cost. So the $6,500 test becomes $6,500 plus $2,200 for retesting, plus scheduling delays that push the retest outside your audit observation period, which means the retest evidence does not count for the current audit cycle anyway. You pay for the retest and still fail the audit.
The missed vulnerability cost. This one is harder to calculate until it happens. A scanner-based engagement at the $6,500 tier does not perform white box source code analysis. It does not trace dataflows. It does not find the Express.js middleware ordering vulnerability where admin routes are registered before authentication applies globally, because that vulnerability produces a normal HTTP 200 response to external probes and matches no CVE signature. It is invisible to any external-only methodology. The average cost of a data breach in 2024 was $4.88 million according to IBM’s Cost of a Data Breach Report. The vulnerability the cheap test missed is the one with the highest probability of being the one that causes it, because it is precisely the class of vulnerability that external-only testing structurally cannot find.
The math is not complicated. The $47,000 full assessment that includes source code analysis, unlimited retests, and a complete SOC 2 evidence package costs less than one enterprise deal lost to a qualified audit opinion, less than one breach notification, and less than one quarter of the average breach cost.
The Hidden Cost Most Teams Discover at Audit Time
The most expensive penetration testing mistake is not choosing the wrong price tier. It is paying for an engagement that does not include the deliverables your compliance framework requires, discovering this during the audit, and paying again.
The deliverables SOC 2 Type II requires that most low-cost assessments do not include:
Retest report. The most commonly missing document. A penetration test report without a retest report tells the auditor that vulnerabilities were identified but their remediation was never independently verified. This can create an evidence gap if the organization's controls require remediation verification. Most traditional firms charge extra for retesting, sometimes as much as 40% of the original engagement cost.
Verification against production specifically. Remediating a finding in staging and retesting there, then deploying to production without another verification cycle, leaves the audited system (production) without retest evidence. If production is the audited environment, confirm whether remediation needs to be verified there and what evidence your auditor expects.
Timeline documentation. A table showing for every finding: discovery date, severity, remediation date, retest date, final status. Without this, the auditor cannot verify SLA compliance. If your policy says critical findings are remediated within 30 days, this document is how you prove it.
Data deletion certificate. Formal confirmation that all data collected during the engagement, including customer records accessed during exploitation, has been permanently destroyed. Auditors reviewing vendor management controls (CC9.2) increasingly ask for this as evidence that third-party testing firms properly handled sensitive data.
Ask every vendor before signing: are the retest report, timeline documentation, and data deletion certificate included as standard deliverables? If the answer requires a conversation about add-on pricing, factor the full cost into your comparison.
CodeAnt AI’s Pricing Model: Why it’s Different
Traditional penetration testing engagements are generally priced around the defined scope, testing effort, and services included. CodeAnt AI uses a different model for its AI-powered penetration testing offering.
CodeAnt AI charges only for what is found. Low and medium severity findings are included at no cost. High and critical findings are what you pay for. This directly aligns engagement cost with the actual risk discovered in your system.
For a deeper explanation of the model, see our guide to the pentest you only pay for when it finds something.
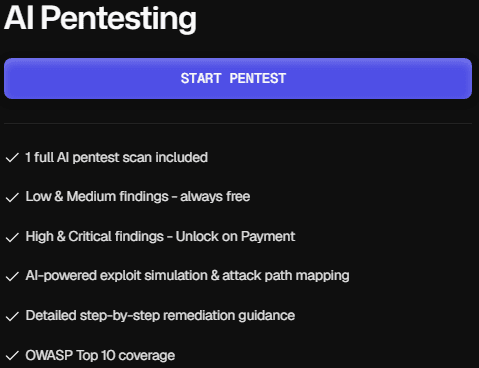
Unlimited retests are included until every finding is confirmed remediated in production. The retest report is a standard deliverable on every engagement. The data deletion certificate is issued on every engagement close. The complete SOC 2 evidence package, all eight required documents, is produced as standard output.
The 48-hour report turnaround makes it operationally viable to run the semi-annual or continuous testing structure that produces the strongest SOC 2 Type II evidence. A traditional engagement with a two-week delivery window and retesting scheduled weeks later creates gaps in observation period coverage. A 48-hour turnaround with same-week retest scheduling closes those gaps.
For a broader comparison of AI-powered penetration testing approaches, see Best AI Penetration Testing Platforms.
Penetration Testing Cost vs Penetration Testing Pricing
The terms penetration testing cost and penetration testing pricing are often used interchangeably, but buyers should think about them slightly differently.
Penetration testing pricing is the vendor's quoted price.
Penetration testing cost is what your organization actually spends to complete the testing lifecycle.
That can include:
Initial assessment
Scope preparation
Engineering support
Retesting
Additional environments
Additional applications
Compliance documentation
Remediation work
Internal coordination
Follow-up testing
A $10,000 assessment that requires another $4,000 retest and substantial internal engineering time can have a higher total cost than a $13,000 assessment that includes those activities.
When comparing quotes, calculate the total testing lifecycle cost, not just the initial invoice.
What Changes the Cost of a Penetration Test?
There is no universal penetration testing price because the amount of work required varies significantly between applications.
A small public-facing application with a few endpoints can be assessed very differently from a multi-tenant SaaS platform with hundreds of APIs, several user roles, cloud infrastructure, and a large source codebase.
The biggest factors affecting penetration testing cost are scope, application complexity, access level, methodology, infrastructure, and deliverables.
Application Size and Scope
Application size is more than the number of pages in a website.
A penetration testing scope can include:
Web applications
APIs
Mobile applications
Public-facing infrastructure
Internal applications
Administrative interfaces
Authentication systems
Cloud services
Third-party integrations
A quote covering one web application is therefore not directly comparable with a quote covering the web application, API layer, cloud infrastructure, and supporting services.
Before comparing prices, ask every provider for a written list of:
Domains and subdomains
Applications
APIs
Environments
IP ranges
Cloud services
User roles
Test accounts
Explicit exclusions
"Your web application" is not a sufficiently detailed scope.
API Surface and Application Complexity
The size and complexity of an API can significantly affect testing effort.
Testers may need to evaluate:
Authentication and session management
Object-level authorization
Role-based permissions
Input validation
Rate limiting
Data exposure
API versioning
File uploads
Administrative endpoints
Business logic
A ten-endpoint application with two roles is fundamentally different from a multi-service SaaS platform with hundreds of endpoints and several permission levels.
This is why API penetration testing should be explicitly listed in the scope rather than assumed to be included in a general web application test.
For example, our IDOR vulnerabilities guide explains how authorization flaws can arise when applications correctly authenticate a user but fail to enforce access controls on individual objects.
Authentication, Roles, and Multi-Tenancy
The number of user roles can increase testing complexity because each role introduces additional authorization boundaries.
A SaaS application might contain:
Standard users
Managers
Administrators
Support users
Billing users
Organization owners
A tester may need to determine what each role can access, modify, approve, delete, or administer.
Multi-tenant applications add another dimension. Testing needs to establish whether one tenant can access another tenant's records, files, API objects, or administrative functionality.
This is why a quote stating "authenticated testing included" is not enough. Ask which roles, tenants, workflows, and endpoints will actually be tested.
For a broader explanation of how black box, gray box, and white box testing differ, see The 3 Types of Penetration Testing and How to Pick the Right One.
Black Box, Gray Box, or White Box Access
The tester's level of access also affects penetration testing pricing.
Black box testing evaluates what an external attacker can discover without privileged internal knowledge.
Gray box testing provides authenticated or limited internal context, allowing deeper testing of authorization, privilege boundaries, and application workflows.
White box testing provides access to source code and implementation details, allowing testers to investigate vulnerabilities that may be difficult to identify externally.
The more internal context a methodology provides, the more questions the tester can investigate. That can increase both the depth and duration of the assessment.
Source Code and CI/CD Access
Source-code access changes the nature of the assessment.
A white-box engagement may examine:
Authentication and authorization logic
API controllers
Database queries
Security middleware
Data flows
Dependency usage
Infrastructure-as-code
Dockerfiles
Kubernetes configuration
CI/CD pipelines
Git history
The value is not simply that the tester can "see the code." Source access allows the tester to connect externally observed behavior to its underlying implementation.
For example, an externally observed authorization failure might be traced to an incorrect permission check, middleware ordering, missing authorization condition, or insecure default.
That additional analysis should be reflected in the scope and price.
Cloud and Infrastructure Complexity
Modern SaaS applications often depend on infrastructure beyond the web application itself.
Depending on the engagement, the attack surface may include:
AWS, Azure, or GCP services
Kubernetes
Containers
Object storage
IAM policies
Load balancers
Databases
Serverless functions
CI/CD infrastructure
Publicly exposed services
A web application penetration test does not automatically mean the underlying cloud environment is being tested.
If infrastructure security is part of your risk model, confirm exactly which cloud assets and configurations are included.
Business Logic and Attack-Path Testing
Some vulnerabilities depend on how the application is supposed to work rather than on a known technical signature.
Examples include:
Bypassing approval workflows
Changing another user's account information
Accessing another tenant's data
Manipulating prices or quantities
Reusing privileged tokens
Skipping required workflow steps
Combining multiple weaknesses into a higher-impact attack path
These scenarios often require authenticated access, application context, and manual reasoning.
When comparing penetration testing quotes, ask explicitly whether business logic testing and attack-path analysis are included.
Retesting and Remediation Verification
Finding vulnerabilities is only one part of the penetration testing lifecycle.
After developers fix findings, remediation needs to be verified.
Ask:
Is retesting included?
How many retest cycles are included?
Is production retesting available?
Are reopened findings covered?
Does the final report document remediation status?
Are additional fees charged for retesting?
A quote that excludes remediation verification may have a lower initial price while creating additional costs later.
Reporting and Compliance Deliverables
The final deliverables can also affect penetration testing pricing.
Depending on your requirements, you may need:
Executive summary
Technical findings
Reproduction steps
Evidence
Severity ratings
Remediation recommendations
Scope documentation
Methodology documentation
Retest report
Compliance mapping
Finding timelines
For organizations using penetration testing as part of a SOC 2 program, confirm which documentation is included in the engagement and which items are optional.
The headline price is therefore only one part of the calculation.
A more useful comparison is:
Scope + methodology + testing depth + validation + remediation verification + deliverables
How to Compare Penetration Testing Quotes
The best way to compare penetration testing pricing is to compare the testing that sits behind the number.
A $10,000 quote and a $20,000 quote may not represent different prices for the same service. One could include authenticated testing, business logic analysis, source-code review, retesting, and detailed evidence, while the other may cover only an external application assessment.
Before choosing a provider, turn every quote into the same set of questions.
Penetration Testing Quote Comparison Checklist
Evaluation area | What to compare |
|---|---|
Applications | Which applications and environments are included? |
APIs | How many endpoints are in scope? Are authenticated APIs included? |
Authentication | Are login, MFA, sessions, password reset, and token flows tested? |
Authorization | Are horizontal and vertical privilege boundaries tested? |
User roles | How many roles and test accounts are included? |
Multi-tenancy | Is cross-tenant access explicitly tested? |
Business logic | Are application-specific workflows tested manually? |
Source code | Is white-box analysis included? |
Cloud | Are AWS, Azure, GCP, Kubernetes, or other infrastructure included? |
Manual testing | How much manual analysis is performed? |
Exploitation | Are suspected vulnerabilities validated through controlled exploitation? |
Attack paths | Are related findings analyzed together for chained impact? |
Reporting | What evidence and remediation guidance are included? |
Retesting | Is remediation verification included? |
Compliance | What documentation is provided for compliance programs? |
Data handling | How is sensitive data handled and deleted after testing? |
Exclusions | Which assets or vulnerability classes are excluded? |
Additional costs | What fees could apply beyond the initial engagement? |
Questions to Ask Before Signing
The most useful questions are often the ones that expose what the quote does not include:
What exactly is in scope?
Which applications, APIs, and environments will be tested?
Are authenticated user flows included?
How many user roles will be tested?
Is multi-tenant authorization testing included?
Are business logic vulnerabilities in scope?
Will source code be reviewed?
Will cloud infrastructure be tested?
How are findings validated?
Is controlled exploitation included?
Is attack-path analysis included?
Is retesting included?
How many retest cycles are included?
What does the final penetration testing report contain?
What compliance documentation is included?
How is sensitive data handled during testing?
What happens if additional assets are discovered?
What is explicitly excluded from the scope?
That last question is particularly important.
A penetration testing proposal should make exclusions visible before the engagement begins. If an important application, API, environment, vulnerability class, or testing method is excluded, the lower price may simply reflect narrower coverage.
Compare Methodology, Not Marketing Language
Terms such as AI-powered, comprehensive, automated, and continuous do not tell you enough about what the tester actually does.
Instead, ask how the provider handles:
Discovery → Testing → Validation → Exploitation → Attack-path analysis → Reporting → Retesting
For example, if a provider identifies a potential authorization vulnerability, does the engagement include controlled validation? Can the tester demonstrate the actual impact? Does the report explain the affected object, role, endpoint, and root cause? Is remediation subsequently verified?
Those details tell you considerably more about the quality of an engagement than a technology label.
For teams evaluating AI-assisted approaches, compare AI Penetration Testing Platforms on methodology, testing depth, validation, reporting, integrations, and pricing model.
Calculate the Total Testing Lifecycle Cost
Do not compare vendors using the initial assessment price alone.
A more useful calculation is:
Total testing cost = Initial assessment + retesting + additional scope + compliance documentation + internal engineering effort
For example, a lower-priced assessment may exclude retesting or charge separately when additional environments need to be assessed.
A higher-priced engagement may include more of the testing lifecycle in the original scope.
The objective is not to find the lowest quote. It is to determine which quote gives you the coverage you actually need at the lowest reasonable total cost.
What Is the Right Penetration Testing Cost for Your Business?
The cheapest penetration test is not necessarily the best value, and the most expensive engagement is not automatically the deepest.
The right question is:
What security coverage does this price actually buy?
The appropriate budget depends on your application's attack surface, architecture, risk profile, compliance requirements, and how frequently the environment changes.
Match the Testing Approach to the Risk
If your primary goal is... | Consider |
|---|---|
Validate what an external attacker can discover | Black box testing |
Test roles, permissions, and tenant isolation | Gray box testing |
Identify source-level security weaknesses | White box testing |
Connect external, authenticated, and code-level findings | Full assessment |
Validate security repeatedly as the application changes | Continuous or recurring testing |
Choose Black Box Testing When
Black box testing is appropriate when your primary question is:
"What could an external attacker discover and exploit?"
It is useful for:
Internet-facing applications
Public APIs
External infrastructure
Newly launched applications
External attack-surface validation
It provides an attacker-perspective assessment without requiring source-code access.
Choose Gray Box Testing When
Gray box testing is particularly valuable when authorization and business logic are major concerns.
Consider it when your application has:
Multiple user roles
Authenticated APIs
Multi-tenant architecture
Complex permissions
Sensitive workflows
Privileged administrative functions
For SaaS companies, this approach can provide deeper validation of whether users can access data or functionality outside their intended permissions.
Choose White Box Testing When
White box testing makes sense when you need to understand not only what is vulnerable but also why.
It is particularly useful when:
Authentication logic is complex
Authorization is implemented across multiple services
Source-level root cause matters
The application handles sensitive data
CI/CD and infrastructure configuration are security-sensitive
External testing alone does not provide sufficient coverage
Source access can also make remediation more actionable because findings can be connected to specific implementation patterns.
Choose a Full Assessment When
A full assessment makes sense when risk spans multiple layers of the technology stack.
For example, a business-critical SaaS platform may need:
External attack-surface testing
Authenticated application testing
Multi-tenant authorization testing
API testing
Source-code analysis
Cloud and infrastructure testing
Attack-path analysis
The advantage is that findings from one perspective can inform testing from another.
An API discovered during external reconnaissance can be tested with authenticated accounts. A vulnerability discovered through those flows can then be traced back to the source code to establish root cause.
For a deeper explanation of how these approaches fit together, see The 3 Types of Penetration Testing and How to Pick the Right One.
Choose Continuous Penetration Testing When
Continuous or recurring penetration testing becomes more relevant as application change increases.
If your team deploys frequently, the attack surface can change substantially between periodic assessments. Recurring testing can help validate changes such as:
New releases
Newly exposed endpoints
Authentication changes
Authorization changes
Infrastructure changes
New integrations
Security fixes
Continuous testing does not necessarily mean eliminating independent periodic assessments. A security program may combine periodic comprehensive testing with recurring or release-aligned validation.
Read Continuous Penetration Testing vs Annual Pentesting for a deeper comparison of the two models.
A Simple Decision Framework
If you are still unsure which approach fits your organization, start with the risk you need to validate:
Need an external attacker perspective?
Start with black box testing.
Most concerned about roles, permissions, or tenant isolation?
Prioritize gray box testing.
Need source-level root cause?
Add white box testing.
Have a large, business-critical application?
Consider an integrated assessment covering external, authenticated, and source-level testing.
Deploy frequently and need recurring validation?
Consider continuous or release-aligned penetration testing.
The right penetration testing cost is therefore not a universal number. It is the cost of achieving the coverage, validation, evidence, and testing frequency your risk profile requires.
Five Questions to Answer Before Choosing a Provider
Before signing a penetration testing contract, you should be able to answer:
What exactly will be tested?
Which vulnerability classes are in scope?
How will findings be validated?
How will remediation be verified?
What evidence will we receive when the engagement is complete?
If you cannot answer those questions from the proposal, the quote is not detailed enough to compare.
And if you're comparing traditional penetration testing with AI-assisted approaches, don't compare only the headline price. Compare coverage, methodology, validation, retesting, reporting, and total lifecycle cost.
For teams evaluating AI-powered alternatives, see Best AI Penetration Testing Platforms.
Find More With CodeAnt AI
CodeAnt AI combines AI-powered penetration testing with automated security analysis to help teams identify and validate vulnerabilities across their applications and infrastructure.
Instead of treating penetration testing as a once-a-year checkbox, teams can use CodeAnt to bring security validation closer to the software development lifecycle.
Explore CodeAnt AI's penetration testing platform to see how AI-powered testing can help your team discover vulnerabilities, validate real security risk, and move from findings to remediation faster.
If your application changes every week, your security testing should not wait until next year.
Start your CodeAnt AI security assessment.

