Deploy fully on-prem or inside your AWS, GCP, or Azure environment. No data ever leaves.
Trusted by Startups to Fortune 100


[ ENTERPRISE SECURITY ]
Built for Enterprise Security

On-prem or Multi-cloud
Deploy in your VPC on AWS, GCP, or Azure or fully on-premises.

Single sign-on (SSO)
Authenticate through your existing identity provider with SAML or OIDC.

Role-based access control
Role and repository-based permissions for developers, security leads, and auditors.
Zero data retention
Code is analyzed in memory, not stored. We keep findings metadata only.

Audit logs and reporting
Log every scan, access, and change. Export to CSV or SIEM.
SOC 2 and HIPAA compliant
Controls are audited yearly, with a signed BAA. Reports are shared under NDA.
[CUSTOMER STORIES]
"CodeAnt went deeper than any penetration test we've ever commissioned. The most thorough offensive security platform we've used."

Jeson Patel
CTO, 11x (Series B, $75M+ Raised)

[OFFENSIVE]
See what
an attacker sees.
Agents chain findings into working exploit paths across your live attack surface, so severity scores stop being the thing you argue about.
START PENTEST

[DEFENSIVE]
Caught before merge,
not after the incident.
Code, dependencies, and cloud config checked in the PR, ranked by real exposure rather than raw CVSS.
START PENTEST










[SECURE & COMPLIANT]
SOC 2 Type II

Gartner Cool Vendor 2026

HIPAA Compliant
[IN THE WILD]
In the wild
The word is spreading read about us in the news below.
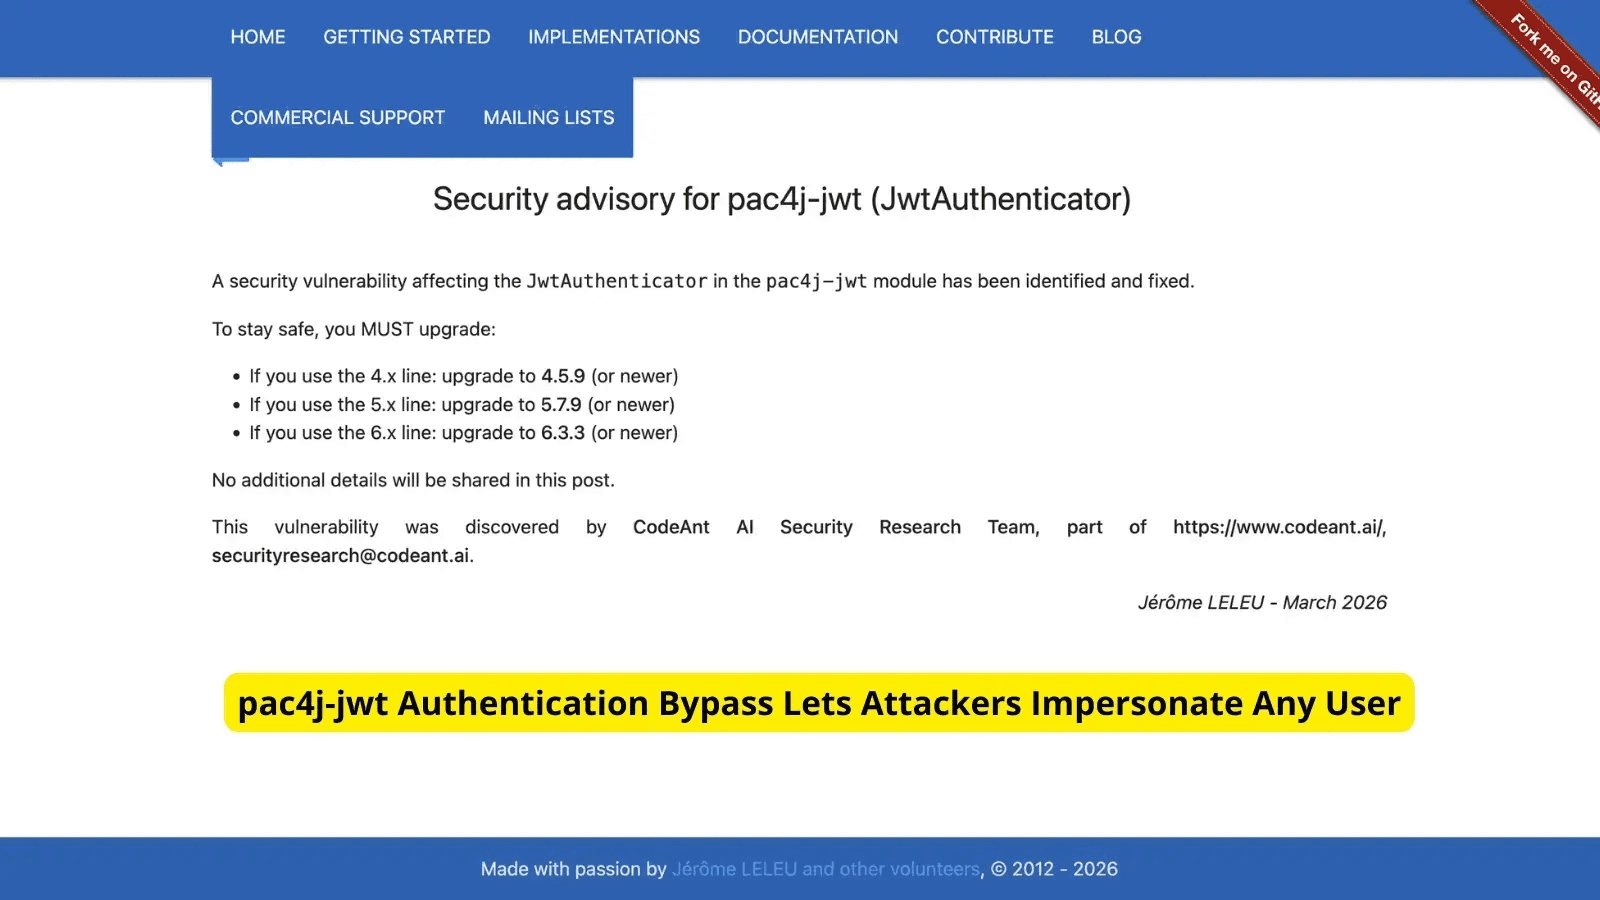
ARTICLE - CYBERNEWS
Critical pac4j-jwt Authentication Bypass Lets Attackers Impersonate Any User

ARTICLE - FINTECH GLOBAL
AI code review platform CodeAnt AI raises $2m to speed up software development

ARTICLE - FORBES
Worried About AI-Generated Code? Ask AI To Review It

ARTICLE - analyticsindiamag
CodeAnt Aims to ‘Stand on the Shoulders of AI Coding Giants’

ARTICLE - ECONOMIC TIMES
How CodeAnt is tackling code review bottlenecks created by AI

ARTICLE - THE SAAS NEWS
CodeAnt AI Raises $2 Million in Seed Round
[GET STARTED]
Ship clean and
secure code faster
START PENTEST

